An Ingress is an HTTP routing rule: it tells a controller to send the requests that carry a given host and path to a given Service. This lesson has you install the Traefik controller on a kind cluster, publish two applications behind a single host name, switch to HTTPS, then break the configuration on purpose so you know where to look when nothing answers. It is for readers who already know how to create a Deployment and a Service and want to expose them outside the cluster.
What you will learn
- Tell the Ingress resource apart from the controller that implements it, and install a controller
- Choose between Ingress and Gateway API, and explain why ingress-nginx is no longer a choice for a new cluster
- Write an Ingress with
ingressClassNamethat routes two applications by path, then by host - Test an Ingress from your machine on the right port (8080 on kind, not 80)
- Declare the
tlsblock of an Ingress and place thekubernetes.io/tlsSecret in the right namespace - Recognize that an annotation depends on the controller
- Diagnose an Ingress that does not respond, from the HTTP code and the controller log
Prerequisites
You have read Kubernetes Services: you know what a Service is, its selector and its EndpointSlices. The versions used are kind 0.33.0, kubectl 1.37.0, nodes in v1.37.0 and Helm 4.3.0.
Helm is only used here to install the Traefik controller. The "Install Helm" section gives the installation in a few commands, and the Helm course (in French) teaches it in detail.
Some names in this lesson are in French on purpose, so that the commands and outputs stay those of the tested cluster: demo-expo means "expo-demo" (exposure demo), nexiste-pas "does-not-exist", par-hote "by-host", ingress-hotes.yaml "ingress-hosts.yaml" and demo-tls-ailleurs "demo-tls-elsewhere".
How does an Ingress work?
A request never enters the Ingress object: it enters the controller's Pod. The Ingress is only a configuration object stored in the Kubernetes API. The controller, here Traefik, watches the Ingress objects, the Services and the addresses of their Pods, rebuilds its routing table when they change, and sends each request to a Pod of the Service it names.
The following diagram shows the path of a request from your machine to the application on this lesson's cluster. Look at the dotted line: it is the only link between the Kubernetes API and the controller, and it is how the rules of the Ingress arrive.
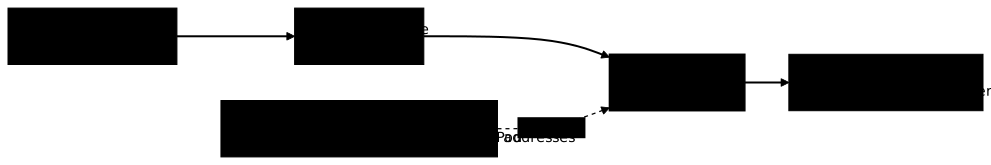
Without a controller, an Ingress is accepted by the API but has no effect, and nothing warns you. A fresh kind cluster has none: kubectl get ingressclass answers No resources found.
Ingress or Gateway API: which one to choose?
The Ingress API is stable but frozen: Kubernetes adds no more features to it and recommends Gateway API for advanced needs (Kubernetes documentation). The two APIs coexist in a cluster and one controller can serve both. What Ingress cannot express (redirects, rewrites, traffic splitting) goes through annotations specific to each controller, whereas Gateway API describes it in its own resources.
| Your need | Reasonable choice |
|---|---|
| Publish an application by host and path, with TLS | Ingress |
| Existing cluster already organized around Ingress | Ingress, migration to plan |
| Redirect, weighted splitting, header matching without annotations | Gateway API |
| Separate the cluster operator's role from the application teams' role | Gateway API |
Why not choose ingress-nginx?
The community project ingress-nginx has been archived since March 24, 2026: its repository is read-only and it no longer receives security fixes (announcement from SIG Network). For a new cluster, choose a maintained controller. This lesson uses Traefik, the controller of the course labs, which also serves Gateway API. Do not confuse ingress-nginx with F5's NGINX Ingress Controller, a separate and maintained product.
Install an Ingress Controller
Installing a controller takes two things: a cluster whose ports are reachable from your machine, then the controller itself. On kind, the nodes are Docker containers and nothing is published by default, so the first step is prepared before creating the cluster.
Prepare a kind cluster that publishes ports 8080 and 8443
This kind-expo.yaml file asks kind to link ports 8080 and 8443 of your machine to ports 80 and 443 of a single worker. The controller will then have to run on that worker.
kind: ClusterapiVersion: kind.x-k8s.io/v1alpha4nodes: - role: control-plane - role: worker extraPortMappings: - containerPort: 80 hostPort: 8080 listenAddress: "0.0.0.0" - containerPort: 443 hostPort: 8443 listenAddress: "0.0.0.0" - role: worker - role: workerkind create cluster --name demo-expo --image kindest/node:v1.37.0@sha256:a1ed56cfb0e7b93589bdf97c8cd566405a265939e3620fc4f5de89adff580ae5 --config kind-expo.yamlkubectl wait --for=condition=Ready nodes --all --timeout=120skubectl create namespace ws-ingressThe four nodes become Ready in about forty seconds. Then read the address of the worker that carries the ports, you will need it to install Traefik.
kubectl get nodes -o wideNAME STATUS ROLES AGE VERSION INTERNAL-IP EXTERNAL-IP OS-IMAGE KERNEL-VERSION CONTAINER-RUNTIMEdemo-expo-control-plane Ready control-plane 24s v1.37.0 172.18.0.3 <none> Debian GNU/Linux 13 (trixie) 6.12.115+deb13.1-amd64 (amd64) containerd://2.3.4demo-expo-worker Ready <none> 16s v1.37.0 172.18.0.4 <none> Debian GNU/Linux 13 (trixie) 6.12.115+deb13.1-amd64 (amd64) containerd://2.3.4demo-expo-worker2 Ready <none> 16s v1.37.0 172.18.0.2 <none> Debian GNU/Linux 13 (trixie) 6.12.115+deb13.1-amd64 (amd64) containerd://2.3.4demo-expo-worker3 Ready <none> 16s v1.37.0 172.18.0.5 <none> Debian GNU/Linux 13 (trixie) 6.12.115+deb13.1-amd64 (amd64) containerd://2.3.4Look at the demo-expo-worker line: its internal address is 172.18.0.4 on this cluster. The addresses of your cluster may differ, and yours is the one to put in the install command.
The port to query is 8080, not 80
This is the mistake that makes you think something is broken when the cluster is healthy. Only the mapped worker publishes the ports, and on your machine they are called 8080 and 8443. The following command shows it.
docker port demo-expo-worker80/tcp -> 0.0.0.0:8080443/tcp -> 0.0.0.0:8443As long as no controller is listening, both ports answer badly, each in its own way. On 8080, the connection is accepted and then cut; on port 80 of your machine, which nothing links to the cluster, it is refused.
curl -sS -m 3 -o /dev/null -w '%{http_code}\n' http://localhost:8080/curl -sS -m 3 -o /dev/null -w '%{http_code}\n' http://localhost/curl: (56) Recv failure: Connection reset by peer000curl: (7) Failed to connect to localhost port 80 after 0 ms: Could not connect to server000Remember the two curl error codes: 56 means the port is linked to the cluster but no controller answers there yet, and 7 means nothing listens on that port of your machine. If a response arrives on port 80 although you installed nothing, it comes from another service on your machine.
Install Helm
Helm is a tool that installs an application on Kubernetes from a package called a chart. It is only used here to install the controller: the guide Helm in 15 minutes (in French) explains it if you want to go further. The following commands download version 4.3.0 from the official site, check its SHA-256 sum, then install the binary in /usr/local/bin.
curl -fsSLo helm-v4.3.0-linux-amd64.tar.gz https://get.helm.sh/helm-v4.3.0-linux-amd64.tar.gzcurl -fsSLo helm-v4.3.0-linux-amd64.tar.gz.sha256sum https://get.helm.sh/helm-v4.3.0-linux-amd64.tar.gz.sha256sumsha256sum -c helm-v4.3.0-linux-amd64.tar.gz.sha256sumtar -xzf helm-v4.3.0-linux-amd64.tar.gz linux-amd64/helmsudo install -m 0755 linux-amd64/helm /usr/local/bin/helmhelm version --shorthelm-v4.3.0-linux-amd64.tar.gz: OKv4.3.0+gbec5b06Look at the OK line: it proves that the downloaded archive matches the published sum, so it has not been modified. If sha256sum answers FAILED, do not install it and download again. These commands apply to a Linux amd64 machine; for another system, take the matching archive from get.helm.sh.
Install Traefik
The following command installs Traefik v3.7.18, with Helm chart 41.6.0, and the image pinned by its digest. Replace 172.18.0.4 with the worker address you read earlier.
helm repo add traefik https://traefik.github.io/chartshelm repo update traefik
helm upgrade --install traefik traefik/traefik \  --namespace traefik --create-namespace --version 41.6.0 \  --set ports.web.nodePort=30080 \  --set ports.web.port=80 \  --set ports.websecure.nodePort=30443 \  --set ports.web.hostPort=80 \  --set ports.websecure.hostPort=443 \  --set 'nodeSelector.kubernetes\.io/hostname=demo-expo-worker' \  --set providers.kubernetesIngress.publishedService.enabled=false \  --set providers.kubernetesIngress.ingressEndpoint.ip=172.18.0.4 \  --set deployment.replicas=1 \  --set image.digest=sha256:9c437ac4f09ce6f4980a8544902d3475fdf70a1a7c578729581d2535dfa7d635 \  --set versionOverride=v3.7.18 \  --set-string 'podSecurityContext.sysctls[0].name=net.ipv4.ip_unprivileged_port_start' \  --set-string 'podSecurityContext.sysctls[0].value=0' \  --set providers.kubernetesGateway.enabled=false \  --set gateway.enabled=false \  --wait --timeout 6mkubectl -n traefik rollout status deployment/traefik --timeout=300s
Three settings link Traefik to your machine. ports.web.hostPort=80 and ports.websecure.hostPort=443 make it listen on ports 80 and 443 of the node, the ones that extraPortMappings links to 8080 and 8443. nodeSelector places it on the only worker that carries these ports.
Two remarks on the command. The quotes around nodeSelector are necessary: without them, the shell swallows the backslash and Helm rejects the option. As for ingressEndpoint.ip, it sets the address that Traefik will copy into the ADDRESS column of the Ingresses.
The installation takes about twenty seconds. The chart notes show a warning about a "non-standard version", v3.7.13. That is the chart's default version, quoted despite versionOverride: the image actually started is the one from the digest, which the following command checks.
kubectl -n traefik get pods -o widekubectl -n traefik get deployment traefik -o jsonpath='{.spec.template.spec.containers[0].image}{"\n"}'NAME READY STATUS RESTARTS AGE IP NODE NOMINATED NODE READINESS GATEStraefik-65f84d5855-b5mxs 1/1 Running 0 19s 10.244.1.2 demo-expo-worker <none> <none>docker.io/traefik@sha256:9c437ac4f09ce6f4980a8544902d3475fdf70a1a7c578729581d2535dfa7d635Check two things in this output: a single traefik Pod is 1/1 Running, on demo-expo-worker, and the image carries the digest you asked for. Then look at the chart's Service, and the classes it created.
kubectl -n traefik get svc traefikkubectl get ingressclassNAME TYPE CLUSTER-IP EXTERNAL-IP PORT(S) AGEtraefik LoadBalancer 10.96.125.80 <pending> 80:30080/TCP,443:30443/TCP 19sNAME CONTROLLER PARAMETERS AGEtraefik (default) traefik.io/ingress-controller <none> 19sThe chart's Service is of type LoadBalancer and stays at EXTERNAL-IP <pending>, since kind has no load balancer. This does not matter here, because access goes through the hostPort, not through the Service. A traefik IngressClass was created by the chart, with the controller traefik.io/ingress-controller. You therefore do not have to write it.
The chart also marks it as the default class, which (default) indicates. According to the Kubernetes documentation, an Ingress without ingressClassName is then handled by the default class.
Traefik goes further: it also serves an Ingress without a class when its own class is not marked as default, a behavior that depends on the controller and not on Kubernetes. Still write the class name in every Ingress, so that the choice of controller depends neither on the cluster setting nor on a Traefik quirk.
One last check tells you whether the controller answers, even before any rule exists.
curl -sS -i -m 3 http://localhost:8080/HTTP/1.1 404 Not FoundContent-Type: text/plain; charset=utf-8X-Content-Type-Options: nosniffDate: Thu, 12 Nov 2026 09:00:38 GMTContent-Length: 19
404 page not foundA 404 page not found in text/plain is Traefik's answer when no rule matches. This code is a good sign at this stage: port 8080 does reach the controller, only a rule is missing.
Create your first Ingress
An Ingress does not name Pods but a Service, which must therefore exist before it. Creating the Ingress first produces no error when the manifest is applied, but requests fail until the Service and its Pods exist. The order is therefore the application, its Service, then the Ingress.
Prepare the application and the Service
Two nginx applications each serve a page that carries their name, in the ws-ingress namespace. Each ConfigMap holds the index.html file, mounted in a folder named after the application (/a or /b), which tells you who answered.
First create the two ConfigMaps. The manifest of the Deployments and Services that follows is saved in the apps.yaml file, which the kubectl apply -f apps.yaml command will then read.
kubectl -n ws-ingress create configmap page-a --from-literal=index.html='application A'kubectl -n ws-ingress create configmap page-b --from-literal=index.html='application B'apiVersion: apps/v1kind: Deploymentmetadata: name: app-a namespace: ws-ingressspec: replicas: 1 selector: matchLabels: app: app-a template: metadata: labels: app: app-a spec: containers: - name: nginx image: nginx:1.30.5@sha256:9bf97bd7714f5e24c1ccd545ecb9eb5435cb6d109c97cebb15e7e455e0239edb ports: - containerPort: 80 volumeMounts: - name: page mountPath: /usr/share/nginx/html/a volumes: - name: page configMap: name: page-a---apiVersion: v1kind: Servicemetadata: name: app-a namespace: ws-ingressspec: selector: app: app-a ports: - port: 80 targetPort: 80---apiVersion: apps/v1kind: Deploymentmetadata: name: app-b namespace: ws-ingressspec: replicas: 1 selector: matchLabels: app: app-b template: metadata: labels: app: app-b spec: containers: - name: nginx image: nginx:1.30.5@sha256:9bf97bd7714f5e24c1ccd545ecb9eb5435cb6d109c97cebb15e7e455e0239edb ports: - containerPort: 80 volumeMounts: - name: page mountPath: /usr/share/nginx/html/b volumes: - name: page configMap: name: page-b---apiVersion: v1kind: Servicemetadata: name: app-b namespace: ws-ingressspec: selector: app: app-b ports: - port: 80 targetPort: 80In this manifest, each Service's port, 80, is the one the Ingress will cite; the targetPort is the one the container listens on.
kubectl apply -f apps.yamlkubectl -n ws-ingress rollout status deployment/app-a deployment/app-b --timeout=90skubectl -n ws-ingress get endpointslicesdeployment.apps/app-a createdservice/app-a createddeployment.apps/app-b createdservice/app-b createdWaiting for deployment "app-a" rollout to finish: 0 of 1 updated replicas are available...deployment "app-a" successfully rolled outdeployment "app-b" successfully rolled outNAME ADDRESSTYPE PORTS ENDPOINTS AGEapp-a-pp6vz IPv4 80 10.244.2.2 13sapp-b-7dpgg IPv4 80 10.244.3.2 13sIn the EndpointSlices, check that each Service has a Pod address in the ENDPOINTS column. A Service without an address will serve nothing, even behind a correct Ingress.
Create the Ingress
This Ingress publishes the two applications under the demo.test host: paths that start with /a go to app-a, those that start with /b go to app-b. The ingressClassName field names the traefik class, so the controller that must handle it. Save the manifest in the ingress-demo.yaml file.
apiVersion: networking.k8s.io/v1kind: Ingressmetadata: name: demo namespace: ws-ingressspec: ingressClassName: traefik rules: - host: demo.test http: paths: - path: /a pathType: Prefix backend: service: name: app-a port: number: 80 - path: /b pathType: Prefix backend: service: name: app-b port: number: 80kubectl apply -f ingress-demo.yamlkubectl -n ws-ingress get ingress demoingress.networking.k8s.io/demo createdNAME CLASS HOSTS ADDRESS PORTS AGEdemo traefik demo.test 172.18.0.4 80 0sThe CLASS column repeats the class, HOSTS the host, and ADDRESS carries 172.18.0.4, the address you passed to ingressEndpoint.ip. This address is a node's, not a cloud load balancer's. It is published by Traefik, which shows that it has seen the Ingress, but it does not prove that requests succeed: the troubleshooting section shows an Ingress that keeps it while its class is wrong.
Test the access
Routing is done on the host name, so the test must send demo.test even though this name exists in no DNS. Two ways allow it: the Host header, or the --resolve option of curl, which maps the name to 127.0.0.1 for that single command. Here the port stays 8080.
curl -sS -i -m 5 -H 'Host: demo.test' http://localhost:8080/a/curl -sS -m 5 -H 'Host: demo.test' http://localhost:8080/b/HTTP/1.1 200 OKAccept-Ranges: bytesContent-Length: 13Content-Type: text/htmlDate: Thu, 12 Nov 2026 09:00:51 GMTEtag: "6af58036-d"Last-Modified: Thu, 12 Nov 2026 09:00:38 GMTServer: nginx/1.30.5
application Aapplication BLook at the body of each response: application A on /a/ and application B on /b/ prove that each path reaches the right application. The Server: nginx/1.30.5 line is the backend's, not the controller's: Traefik does not replace it.
Add two controls to check that routing really depends on the host.
curl -sS -m 5 -o /dev/null -w '%{http_code}\n' http://localhost:8080/a/curl -sS -m 5 --resolve demo.test:8080:127.0.0.1 http://demo.test:8080/a/404application AWithout the demo.test host, the same URL returns 404. With --resolve, the request leaves under the name demo.test and the page answers. One last trap concerns the request to /a without a trailing slash.
curl -sS -i -m 5 -H 'Host: demo.test' http://localhost:8080/aHTTP/1.1 301 Moved PermanentlyContent-Length: 169Content-Type: text/htmlDate: Thu, 12 Nov 2026 09:00:52 GMTLocation: http://demo.test/a/Server: nginx/1.30.5
<html><head><title>301 Moved Permanently</title></head><body><center><h1>301 Moved Permanently</h1></center><hr><center>nginx/1.30.5</center></body></html>This redirect comes from nginx, the backend, which adds the trailing slash to a folder. Look at the Location line: it has no port 8080, so a client that followed the redirect would aim at port 80 and fail. Always test with the trailing slash.
Path routing
Under a single host, several paths target different Services, which lets you expose an API and its web interface without a dedicated subdomain. The path is passed as is to the backend. That is why this lesson's applications serve their page under /a and /b: if they served it at the root, /a/ would be unknown to them and they would answer 404.
The pathType field decides what "match" means. With Prefix, /a matches /a, /a/ and /a/page.html. With Exact, only /a matches. Choose Prefix unless you need otherwise (definition of path types in the Kubernetes documentation).
A path you did not declare leads nowhere. The following test shows it on /c/, with the correct host.
curl -sS -i -m 5 -H 'Host: demo.test' http://localhost:8080/c/HTTP/1.1 404 Not FoundContent-Type: text/plain; charset=utf-8X-Content-Type-Options: nosniffDate: Thu, 12 Nov 2026 09:00:52 GMTContent-Length: 19
404 page not foundThis 404 comes from Traefik, not from the application: the body is a 19-byte plain text, without nginx's HTML page. It signals a request that matches no rule, not a failed backend.
Multi-domain routing
An Ingress accepts several host entries, each with its own paths. In the following example, a.demo.test publishes app-a on /a, and b.demo.test publishes app-b on /b. For a set of applications run by different teams, prefer one Ingress per application: deleting a shared Ingress cuts all its rules at once.
Save this manifest in the ingress-hotes.yaml file.
apiVersion: networking.k8s.io/v1kind: Ingressmetadata: name: par-hote namespace: ws-ingressspec: ingressClassName: traefik rules: - host: a.demo.test http: paths: - path: /a pathType: Prefix backend: service: name: app-a port: number: 80 - host: b.demo.test http: paths: - path: /b pathType: Prefix backend: service: name: app-b port: number: 80kubectl apply -f ingress-hotes.yamlcurl -sS -m 5 --resolve a.demo.test:8080:127.0.0.1 http://a.demo.test:8080/a/curl -sS -m 5 --resolve a.demo.test:8080:127.0.0.1 http://a.demo.test:8080/b/ -o /dev/null -w '%{http_code}\n'ingress.networking.k8s.io/par-hote createdapplication A404The first call returns application A and the second 404, stuck together on the same line because the body of the first response has no line ending. The 404 is normal: the a.demo.test host only publishes /a. A request is routed only if both its host and its path match a rule.
Troubleshooting: an Ingress that does not respond
A failing Ingress is diagnosed from the outside in: does the controller answer, did it keep the rule, does the Service have Pods. The HTTP code already tells you at which stage the chain breaks, which saves you from rereading the YAML when the fault is a Service selector.
Check the Ingress status
The first reflex is to read kubectl get ingress and kubectl describe ingress, but they do not tell everything. The following test gives the demo Ingress a class that does not exist, then reads what the cluster says about it.
kubectl -n ws-ingress patch ingress demo --type merge -p '{"spec":{"ingressClassName":"nexiste-pas"}}'kubectl -n ws-ingress get ingress demokubectl -n ws-ingress describe ingress demoingress.networking.k8s.io/demo patchedNAME CLASS HOSTS ADDRESS PORTS AGEdemo nexiste-pas demo.test 172.18.0.4 80 4sName: demoLabels: <none>Namespace: ws-ingressAddress: 172.18.0.4Ingress Class: nexiste-pasDefault backend: <default>Rules: Host Path Backends ---- ---- -------- demo.test /a app-a:80 (10.244.2.2:80) /b app-b:80 (10.244.3.2:80)Annotations: <none>Events: <none>The patch is accepted without error, Events is empty and ADDRESS keeps 172.18.0.4. Nothing in the object says that nobody handles it anymore. The proof is in the HTTP response: one to two seconds after the patch, the request returns 404.
curl -sS -m 5 -o /dev/null -w '%{http_code}\n' -H 'Host: demo.test' http://localhost:8080/a/404Put the correct class back, and the route returns within a few seconds.
kubectl -n ws-ingress patch ingress demo --type merge -p '{"spec":{"ingressClassName":"traefik"}}'curl -sS -m 5 -o /dev/null -w '%{http_code}\n' -H 'Host: demo.test' http://localhost:8080/a/ingress.networking.k8s.io/demo patched200Depending on when the request leaves, the first response may still be 404: Traefik takes one to two seconds to reread the Ingress. Wait two seconds and try again before concluding.
The ADDRESS column therefore does not prove that an Ingress is handled. The proof that counts is a request that succeeds.
Check the Ingress Controller
The controller says what it is doing in its log, which you read with kubectl logs. A configuration error of an Ingress appears there, whereas it is absent from the object's events. The TLS section gives a real example.
kubectl -n traefik logs deploy/traefik --tail=20If the controller itself does not start, look at its Pods and their events with kubectl -n traefik get pods and kubectl -n traefik describe pod. These are the same steps as for any application.
Common errors
The returned code tells you where the failure is. A Traefik 404 means that no rule matches, a 503 that the rule exists but the Service has no Pod.
To get the 503, remove the Pods of app-a by breaking the selector of its Service. The EndpointSlices empty out, and Traefik answers.
kubectl -n ws-ingress patch service app-a --type merge -p '{"spec":{"selector":{"app":"nexiste-pas"}}}'kubectl -n ws-ingress get endpointslices -l kubernetes.io/service-name=app-acurl -sS -m 5 -i -H 'Host: demo.test' http://localhost:8080/a/service/app-a patchedNAME ADDRESSTYPE PORTS ENDPOINTS AGEapp-a-pp6vz IPv4 <unset> <unset> 20sHTTP/1.1 503 Service UnavailableContent-Type: text/plain; charset=utf-8X-Content-Type-Options: nosniffDate: Thu, 12 Nov 2026 09:01:01 GMTContent-Length: 20
no available serverThe EndpointSlice has neither port nor address anymore, and Traefik answers 503 Service Unavailable with no available server. Put the original selector back to continue.
kubectl -n ws-ingress patch service app-a --type merge -p '{"spec":{"selector":{"app":"app-a"}}}'The table summarizes the symptoms met in this lesson.
| Symptom | Likely cause | Where to look |
|---|---|---|
curl: (7) on port 80 | You aim at port 80 of your machine, linked to nothing | Use 8080 on this cluster |
curl: (56) on port 8080 | The port is linked but no controller listens | kubectl -n traefik get pods |
404 page not found in plain text | No rule matches: host, path or class | kubectl describe ingress, then ingressClassName |
503, no available server | The Service has no Pod | kubectl get endpointslices -l kubernetes.io/service-name=<service> |
No event, 404 after a class change | No controller carries this class | kubectl get ingressclass |
Configure Ingress with TLS
The tls block of an Ingress names a Secret of type kubernetes.io/tls, which must be in the same namespace as the Ingress. The controller reads the certificate and the key there, and serves them for the listed hosts. For the test, a self-signed certificate is enough. In production, cert-manager creates and renews this Secret for you.
openssl req -x509 -newkey rsa:2048 -nodes -days 1 -keyout tls.key -out tls.crt -subj "/CN=demo.test" -addext "subjectAltName=DNS:demo.test"kubectl -n ws-ingress create secret tls demo-tls --cert=tls.crt --key=tls.keykubectl -n ws-ingress get secret demo-tlssecret/demo-tls createdNAME TYPE DATA AGEdemo-tls kubernetes.io/tls 2 0sThe Secret has the type kubernetes.io/tls and two data entries, the certificate and the key. Save the TLS Ingress in the ingress-tls.yaml file. Delete the two previous Ingresses so you keep only this one, then apply it.
apiVersion: networking.k8s.io/v1kind: Ingressmetadata: name: demo-tls namespace: ws-ingressspec: ingressClassName: traefik tls: - hosts: - demo.test secretName: demo-tls rules: - host: demo.test http: paths: - path: /a pathType: Prefix backend: service: name: app-a port: number: 80kubectl delete ingress demo par-hote -n ws-ingresskubectl apply -f ingress-tls.yamlcurl -sS -k -m 5 --resolve demo.test:8443:127.0.0.1 https://demo.test:8443/a/ -v 2>&1 | grep -E 'subject|^< HTTP|application'ingress.networking.k8s.io "demo" deleted from ws-ingress namespaceingress.networking.k8s.io "par-hote" deleted from ws-ingress namespaceingress.networking.k8s.io/demo-tls created* subject: CN=demo.test< HTTP/2 200application ALook at the subject: CN=demo.test line: the certificate presented is yours, and the page answers over HTTP/2. Without the -k option, curl rejects this certificate because no authority signed it.
curl -sS -m 5 --resolve demo.test:8443:127.0.0.1 https://demo.test:8443/a/curl: (60) SSL certificate problem: self-signed certificateMore details here: https://curl.se/docs/sslcerts.html
curl failed to verify the legitimacy of the server and therefore could notestablish a secure connection to it. To learn more about this situation andhow to fix it, please visit the webpage mentioned above.Enabling TLS does not forbid port 80 either. Query the same Ingress over plain HTTP: the page still answers, without a redirect to HTTPS.
curl -sS -i -m 5 -H 'Host: demo.test' http://localhost:8080/a/ | head -5HTTP/1.1 200 OKAccept-Ranges: bytesContent-Length: 13Content-Type: text/htmlDate: Thu, 12 Nov 2026 09:01:08 GMTThe tls block adds HTTPS, it does not remove HTTP. Redirecting HTTP to HTTPS takes a setting specific to the controller, for example Traefik's RedirectScheme Middleware (Traefik documentation). The guide Traefik on Kubernetes (in French) shows how to attach a middleware to a route.
What happens if the Secret is in another namespace?
A Secret placed in a different namespace than the Ingress is not read, and the failure stays quiet. Create a demo-tls-ailleurs Secret in the ws-ingress-b namespace and have the Ingress cite it.
kubectl create namespace ws-ingress-bkubectl -n ws-ingress-b create secret tls demo-tls-ailleurs --cert=tls.crt --key=tls.keykubectl -n ws-ingress patch ingress demo-tls --type merge -p '{"spec":{"tls":[{"hosts":["demo.test"],"secretName":"demo-tls-ailleurs"}]}}'curl -sS -k -m 5 --resolve demo.test:8443:127.0.0.1 https://demo.test:8443/a/ -v 2>&1 | grep -E 'subject|issuer|^< HTTP|SSL|alert'namespace/ws-ingress-b createdsecret/demo-tls-ailleurs createdingress.networking.k8s.io/demo-tls patched* SSL connection using TLSv1.3 / TLS_AES_128_GCM_SHA256 / X25519MLKEM768 / RSASSA-PSS* subject: CN=TRAEFIK DEFAULT CERT* issuer: CN=TRAEFIK DEFAULT CERT* SSL certificate verify result: self-signed certificate (18), continuing anyway.< HTTP/2 200The patch is accepted, the page answers 200, but the certificate is no longer yours: Traefik serves its own certificate, CN=TRAEFIK DEFAULT CERT. With -k, nothing looks broken, and a client that verifies the certificate would refuse the connection. The error is only in the controller's log.
kubectl -n traefik logs deploy/traefik --tail=-1 | grep -i -E 'secret|demo-tls|certificate' | tail -102026-11-12T09:01:04Z INF Updated ingress status ingress=demo-tls namespace=ws-ingress2026-11-12T09:01:08Z ERR Error configuring TLS error="secret ws-ingress/demo-tls-ailleurs does not exist" ingress=demo-tls namespace=ws-ingress providerName=kubernetesRead the ERR line: Traefik looks for the demo-tls-ailleurs Secret in ws-ingress, the Ingress's namespace, and does not find it. Writing secretName: ws-ingress-b/demo-tls-ailleurs is not a solution, the API rejects this name (spec.tls[0].secretName: Invalid value). The solution is to create the Secret in the Ingress's namespace.
kubectl -n ws-ingress patch ingress demo-tls --type merge -p '{"spec":{"tls":[{"hosts":["demo.test"],"secretName":"demo-tls"}]}}'curl -sS -k -m 5 --resolve demo.test:8443:127.0.0.1 https://demo.test:8443/a/ingress.networking.k8s.io/demo-tls patchedapplication AA default certificate that answers 200 therefore proves nothing: read the subject of the presented certificate (openssl s_client or curl -v), not only the HTTP code.
Why are annotations not portable from one controller to another?
Everything the Ingress specification does not cover, such as redirects, address filtering or rewrites, is set through annotations or objects specific to the controller. An annotation from another controller is silently ignored. The following example puts on the Ingress an ingress-nginx annotation, which Traefik does not know.
kubectl -n ws-ingress annotate ingress demo-tls nginx.ingress.kubernetes.io/rewrite-target=/ --overwritekubectl -n ws-ingress describe ingress demo-tls | grep -A3 Annotationscurl -sS -k -m 5 --resolve demo.test:8443:127.0.0.1 https://demo.test:8443/a/ingress.networking.k8s.io/demo-tls annotatedAnnotations: nginx.ingress.kubernetes.io/rewrite-target: /Events: <none>application AThe annotation is accepted, no event is emitted, and the response is unchanged: if the rewrite to / had applied, nginx would have served its welcome page. Annotations therefore make an Ingress hard to port from one controller to another: changing controller forces you to rewrite them, and nothing signals the ones that no longer work. Gateway API describes these behaviors in the API itself.
How do you clean up the lesson's cluster?
Delete the namespaces, the Helm release, then the cluster.
kubectl delete namespace ws-ingress ws-ingress-bhelm uninstall traefik --namespace traefikkind delete cluster --name demo-expoHands-on practice
The two labs of this lesson rely on the same steps, without redoing the demonstration. The first publishes two applications already running under a single host name, app.local, and is validated on what each path answers, including an undeclared path that must lead to neither of them. The second starts from a site that already answers over HTTPS, but with the controller's default certificate: the task is to serve a certificate that really names the host, without breaking the route.
These labs run on a kubeadm virtual machine, with the same Traefik as in the demonstration. Two things differ. Requests go through ports 30080 and 30443 of the node, not through localhost:8080. The traefik class is not marked as default there (isDefaultClass=false): Kubernetes therefore assigns no class to an Ingress that names none, and the lab requires you to name yours, so that the choice of controller is explicit.
As in the demonstration, kubectl get ingress shows the node's address in the ADDRESS column there.
Key takeaways
- An Ingress is a routing rule; without a controller, it is accepted by the API and stays without effect. A fresh kind cluster has neither a controller nor an IngressClass: Traefik's Helm chart creates the
traefikIngressClass. - Always write
ingressClassName, even if the class is marked as default on your cluster. - On this kind cluster, your machine queries port 8080 (HTTP) or 8443 (HTTPS), never port 80 or 443 of your machine.
- A request is routed only if its host and path match a rule; otherwise Traefik answers
404 page not found, and503when the Service has no Pod. ADDRESSdoes not prove that an Ingress is served: only a request that succeeds proves it.- The
kubernetes.io/tlsSecret must be in the Ingress's namespace; otherwise Traefik serves its default certificate, with a200, and the error is only in its log. - An annotation from another controller is ignored without a message: Gateway API avoids this dependency.
ingress-nginxhas been archived since March 24, 2026: for a new cluster, pick a maintained controller such as Traefik.
FAQ: frequently asked questions about Ingress
These questions take up the points of the lesson: the role of the controller, the choice between Ingress and Gateway API, HTTPS and the 404 and 503 codes.
tls block serves HTTPS.The Ingress is only a configuration: requests go through the controller's Pod, never through the Ingress object itself.traefik IngressClass. Another maintained controller is F5's NGINX Ingress Controller, not to be confused with ingress-nginx, the archived community project.- Ingress is enough to publish an application by host and path, with TLS, and on a cluster already organized around Ingress (plan the migration).
- Gateway API fits redirects, weighted traffic splitting or header matching without annotations, and separating the cluster operator's role from the application teams' role.
tls block in the Ingress, which names a Secret of type kubernetes.io/tls. This Secret must be in the same namespace as the Ingress.spec:
ingressClassName: traefik
tls:
- hosts:
- demo.test
secretName: demo-tls
kubectl -n ws-ingress create secret tls demo-tls --cert=tls.crt --key=tls.key. If the Secret is in another namespace, the request still answers 200, but Traefik serves its own certificate and the error only appears in its log. The tls block adds HTTPS without removing HTTP: redirecting one to the other takes a setting specific to the controller.In production, cert-manager (in French) creates and renews this Secret for you.- 404
page not foundin plain text: Traefik found no matching rule. Check the request'shostandpath, and theingressClassName: with a class name that does not exist, the Ingress is accepted,kubectl describe ingressshows no error, and requests return404. - 503
no available server: the rule exists, but the Service has no Pod. A Service selector that matches no Pod empties the EndpointSlices.
kubectl get ingressclass
kubectl -n ws-ingress get endpointslices -l kubernetes.io/service-name=<service>
kubectl -n traefik logs deploy/traefik --tail=20
ingress-nginx has been archived since March 24, 2026: its repository is read-only and it no longer receives security fixes (announcement from SIG Network).- New cluster: choose a maintained controller, such as Traefik, or Gateway API.
- Existing cluster: plan the migration, because any flaw discovered from now on will stay unfixed.
ingressClassName field gives the name of the IngressClass, returned by kubectl get ingressclass, and so names the controller that must handle the Ingress.If the class does not exist, no controller handles the Ingress anymore: the API accepts the object, no event is emitted, and requests return 404.Without the field, Kubernetes gives the Ingress to the class marked as default. Traefik goes further and also serves an Ingress without a class when its own class is not marked as default, but this behavior depends on the controller. So always write the class name, so that the choice of controller is explicit.ADDRESS column does not prove that the Ingress is served. It shows the address the controller publishes on the Ingresses it has seen. In the lesson, ingressEndpoint.ip sets this address, that of a kind node.If you give the Ingress a class that does not exist, kubectl get ingress still shows the address, kubectl describe ingress shows no error, and yet requests return 404.The proof that counts is a request that succeeds: test with curl and read the controller's log.docker port demo-expo-worker
curl -sS -m 5 -H 'Host: demo.test' http://localhost:8080/a/
curl -sS -m 5 --resolve demo.test:8080:127.0.0.1 http://demo.test:8080/a/
Host header or the --resolve option, the same URL returns 404. As for errors, curl: (56) means the port is linked to the cluster but no controller answers there, and curl: (7) that nothing listens on that port of your machine.Test your knowledge
Seven questions drawn from the bank: role of the controller, routing by host and by path, TLS, the ingressClassName field and the port to query on kind.
Knowledge check
Check what you have learned with this interactive quiz
How it works
- The timer starts when you click Start
- Multiple choice, true/false and short answer questions
- You can move between questions
- Detailed results are shown at the end
Starts the quiz and the timer
Review
(0/0)Score by domain
A domain groups several guides and gets several questions, so its score is more reliable than a per-topic score, which often rests on a single question.
Summary
Strengths
No topic passed at 80% on at least two questions yet.
Weak areas
No topic below the pass mark.
Recommended next
Hints before you try again?
Continue the course: Kubernetes Gateway API: Gateway, HTTPRoute and route diagnosis
A new full quiz with random questions
Work again only on the questions you missed