Software supply chain threats fall into families, one per step between writing the code and running it: knowing which family an incident belongs to tells you where to look and which defense to plan. This lesson maps these families, from the producer of the code to the cloud where it runs, with, for each one, what the attacker is after and a real example. It is meant for developers, DevOps engineers, application security specialists and security managers (CISOs) who want an overview before studying a specific attack. The model rests on the SLSA standard v1.2 (a framework of security levels for building and publishing software) and on the catalog of vectors (the concrete paths an attack takes) of the SOCLE approach, this site's open framework of supply chain requirements.
What you will learn
- Place an attack in one of the threat families of the chain, from the producer to the runtime.
- Link an incident to its anchored attack vectors (SLSA v1.2, CNCF, OWASP CICD-SEC, MITRE ATT&CK).
- Recognize the real examples of each family (XZ, SolarWinds, Shai-Hulud, Codecov).
- Find, when it exists, the dedicated guide that goes deeper into an attack.
How to read this model
Where the page understanding cyber threats (in French) answers "who attacks and how" (attacker profiles, the kill chain, which is the sequence of steps of an attack), this lesson answers "where the attacker strikes in the chain". Each family corresponds to a step, from the source code to execution. The vectors cited are anchored in recognized frameworks (SLSA, the CNCF supply chain security paper, OWASP CICD-SEC, the top 10 risks of CI/CD pipelines, and MITRE ATT&CK, a public knowledge base of attacker techniques): this is the principle of the SOCLE approach (in French), which assembles these sources into enforceable requirements. For the associated protection framework, see SLSA (in French) and its official threat model. The detail of each vector (V-GOV-1, V-CI-5 and the others) is in the catalog of SOCLE attack vectors (in French).
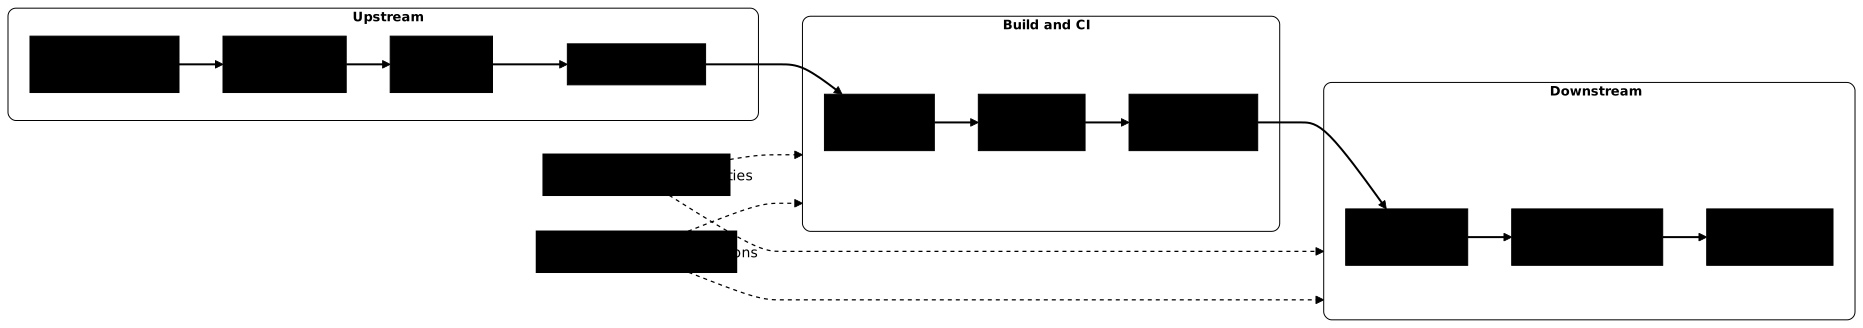
The diagram below shows the thread to follow. Read the three groups from left to right (upstream, build and CI, downstream): each box is a family, and the thick arrow follows the path of the code up to its execution. The two red boxes, secrets and third-party integrations, belong to no single step: their dotted lines show that they touch the build as well as the downstream. The diagram groups some families to stay readable (runners and OIDC, for example): the tables that follow give the detail, family by family.
Upstream: from the producer to the dependencies
The upstream is the ground of insidious attacks: compromising the code before it is built. The XZ Utils case (2024), where a patient maintainer slipped in a backdoor, illustrates the malicious producer; PHP (2021) that of a compromised Git server; event-stream (2018) that of a booby-trapped dependency. The producer case is detailed in malicious producer; the other guides are source code governance, the attacks via package managers and transitive trust. On the defense side, an SBOM (software bill of materials, the list of components) lists what you actually integrated and an artifact firewall filters what can come in.
| Family (SOCLE vectors) | What the attacker is after |
|---|---|
| Producer & governance (V-GOV-1/2/3) | Malicious maintainer, protestware, insider threat |
| Developer workstation (V-WKS-1 to 6) | Booby-trapped IDE extension, fake job interview (Lazarus, a state-sponsored hacker group), curl | sh |
| Source & SCM (V-SRC-1 to 10) | Push without review, pwn request (a pull request that tricks a workflow into running with elevated rights), history rewrite, script injection |
| Dependencies (V-DEP-1 to 7) | Typosquatting, dependency confusion, postinstall scripts, transitive |
Build and CI: the pipeline as a target
The integration pipeline runs code at every commit: it is a prime point of compromise. Poisoned pipeline execution attacks (PPE: making the pipeline run code chosen by the attacker) and the hijacking of legitimate tools are detailed in Living Off The Pipeline and in environment variable poisoning; the overview is the OWASP Top 10 CI/CD. The tj-actions incident (2025) showed the danger of an unpinned third-party action.
| Family (SOCLE vectors) | What the attacker is after |
|---|---|
| Poisoned execution (PPE) (V-CI-1 to 4) | Modify a workflow, a Makefile or a test that gets executed; poison the cache |
| Compromised runners (V-CI-8 to 12) | Persistent runner, exposed Docker socket, container escape |
| OIDC & third-party actions (V-CI-5/6/7) | Theft of the OIDC token, unpinned action, build from a fork |
| Packaging & artifacts (V-PKG-1 to 4) | Artifact altered after the build, poisoned base image, rewritten mutable tag |
Downstream: from the release to the runtime
Once the artifact is produced, the attacker targets its publication, its distribution and its execution. SolarWinds (2020) remains the typical example of a valid provenance on a booby-trapped artifact; Shai-Hulud that of a worm that automatically republishes a maintainer's packages using stolen tokens. Defense by verification is covered in SLSA (in French) and in from provenance to policy.
| Family (SOCLE vectors) | What the attacker is after |
|---|---|
| Release, provenance & signing (V-REL-1 to 4) | Theft of the signing key, forged provenance, absence of verification |
| Registries & publication (V-REG-1 to 5) | Publisher account takeover, stolen publishing token, republishing worm |
| Distribution & consumption (V-DIST-1 to 5) | Altered CDN or mirror, signed but trojanized installer |
| Deployment & admission (V-ADM-1 to 3) | Unverified artifact deployed, admission policy in warning-only mode |
| Runtime & operations (V-RUN-1 to 3) | Exfiltration, lateral movement, wiper (destructive malware) |
Cross-cutting: secrets and integrations
Two families run through the whole chain. Secrets are a prime target: a stolen token opens everything else, as Capital One showed through the IMDS (the metadata service of a cloud instance, which hands it its temporary credentials). Third-party integrations (OAuth apps, GitHub Apps, pipeline services) offer durable and discreet access: Codecov (2021) exfiltrated the CI variables of thousands of projects, Vercel illustrates the abuse of an OAuth app. The cross-cutting reference remains the OWASP Top 10 CI/CD.
| Family (SOCLE vectors) | What the attacker is after |
|---|---|
| Secrets & identities (V-SEC-1 to 6) | Plaintext secret, long-lived token, overly broad OIDC, IMDS, toxic IAM combination |
| Integrations & third parties (V-INTEG-1 to 3, V-CI-13) | Compromised OAuth app, abused GitHub App, hijacked pipeline service |
Emerging: AI and cloud
Two families are on the rise. On the AI/ML side, models and agents are becoming artifacts in their own right: data or weight poisoning, prompt injection, and booby-trapped agent tools, including the threats specific to the Model Context Protocol (in French) (tool poisoning; confused deputy, an agent tricked into using its own rights on behalf of an attacker). On the cloud side, the final link concentrates exfiltration and privilege escalation techniques.
| Family (SOCLE vectors) | What the attacker is after |
|---|---|
| AI / ML (V-IA-1 to 8) | Data/model poisoning, prompt injection, RAG poisoning, MCP agent tool |
| Cloud & container posture (V-CLD-1 to 16) | IMDS access, storage exfiltration, toxic IAM combination, K8s escape, cluster-to-cloud pivot |
Key points
- Supply chain threats can be mapped into families, from the producer to the cloud: each one corresponds to a step where the attacker strikes.
- The vectors are anchored (SLSA v1.2, CNCF, OWASP CICD-SEC, MITRE ATT&CK).
- Secrets and third-party integrations cross the whole chain.
- Several families already have a dedicated guide (producer, package managers, LOTP for Living Off The Pipeline, env poisoning, OWASP CI/CD); for the others, the tables give the vectors to look up in the SOCLE catalog.
- Understanding where the attacker strikes is the first step of the approach: threat, then requirement, then evidence.
Knowledge check
Check that the essentials of this lesson are in place. The questions only cover what has just been explained here.
Knowledge check
Check what you have learned with this interactive quiz
How it works
- The timer starts when you click Start
- Multiple choice, true/false and short answer questions
- You can move between questions
- Detailed results are shown at the end
Starts the quiz and the timer
Review
(0/0)Score by domain
A domain groups several guides and gets several questions, so its score is more reliable than a per-topic score, which often rests on a single question.
Summary
Strengths
No topic passed at 80% on at least two questions yet.
Weak areas
No topic below the pass mark.
Recommended next
Hints before you try again?
Continue the course: Malicious producer: XZ, protestware, insider threat
A new full quiz with random questions
Work again only on the questions you missed